Revesery
Dashboard
Home
Explore
Groups
Tools
Task
Social Media
VideoBulk VideoProfile PictureSlide ShowSound / AudioUnfollowersDouyin
VideoBulk Video
VideoStoriesBulk VideoProfile PictureSlide ShowUnfollowersStalker CheckSoon
VideoUnfollowers
MP4 · VideoMP3 · Audio
WhatsApp
Profile PictureCover Art & Preview
Profile Picture
Video & Image
Video & Photo
Utilities
AI Chat
Fake SNBTWatermark KTP
TeraboxVidey
Deep Voice CheckerReview Calculator
Surat IzinQR GeneratorSoon
Case ConverterCookie Converter
Request a toolImage ToolsSoonText ToolsSoon
Premium
Soon
Add bookmarks
Revesery
HomeExploreTrendingGroupsContributors
⌘K

Most read

Nothing published yet — type a topic and we’ll dig.
ShareLogin
Back to feed
AR
Alex RuiezExpert
@alex · Sep 21, 2026 · 3 views
#Tools

How to Test for Auth Precedence Flaws in Your API

Most auth bypasses aren't in the main login flow. They hide in fallback paths nobody remembers — endpoints that read a token from the header but will also accept it as a cookie or a query parameter. This share is the two-request test that finds that gap, plus the fix that closes it.

Every order of precedence is its own attack surface. One endpoint checks the header, another checks the cookie, and the same user ends up with two identities. That gap is the bug.

Tutorial

  1. Send a single request carrying two different tokens. Put one in the Authorization header and one in a cookie.
  2. Swap the two tokens and send the same request again. Keep everything else about the request identical.
  3. Watch whether the app accepts either token. If it accepts either one, you found a precedence flaw.
  4. Pick one auth source and reject everything else. The fix is boring, and that is the point.
  5. Log the rejected fallbacks. Those rejections are the ones worth watching.
  6. Delete the legacy paths that still authenticate, or version lock them out. Legacy paths are where attackers live.

Wrapping Up

You now have a test that costs two requests and a fix that costs one decision: one auth source, everything else rejected. Run it against the endpoints you have forgotten about, because the same user with two identities is the one that slips through. Then log what you reject and remove what you no longer need.

Liked Alex Ruiez's share? Revesery is where people swap what they're actually building.

Join with Google
Be the first to sayBe first

Does this still work?

Nobody's checked yet

Sign in to tell everyone how it went.

Continue with Google

Be the first — one tap saves the next person an hour.

It takes 3 reports in 30 days to set the status.

Comments

Join the conversation — sign in to comment.

Sign In Now

No comments yet — start the conversation!

More shares you might like

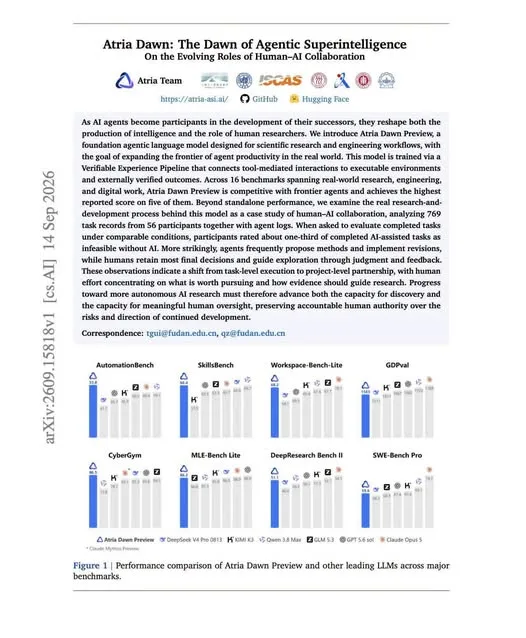
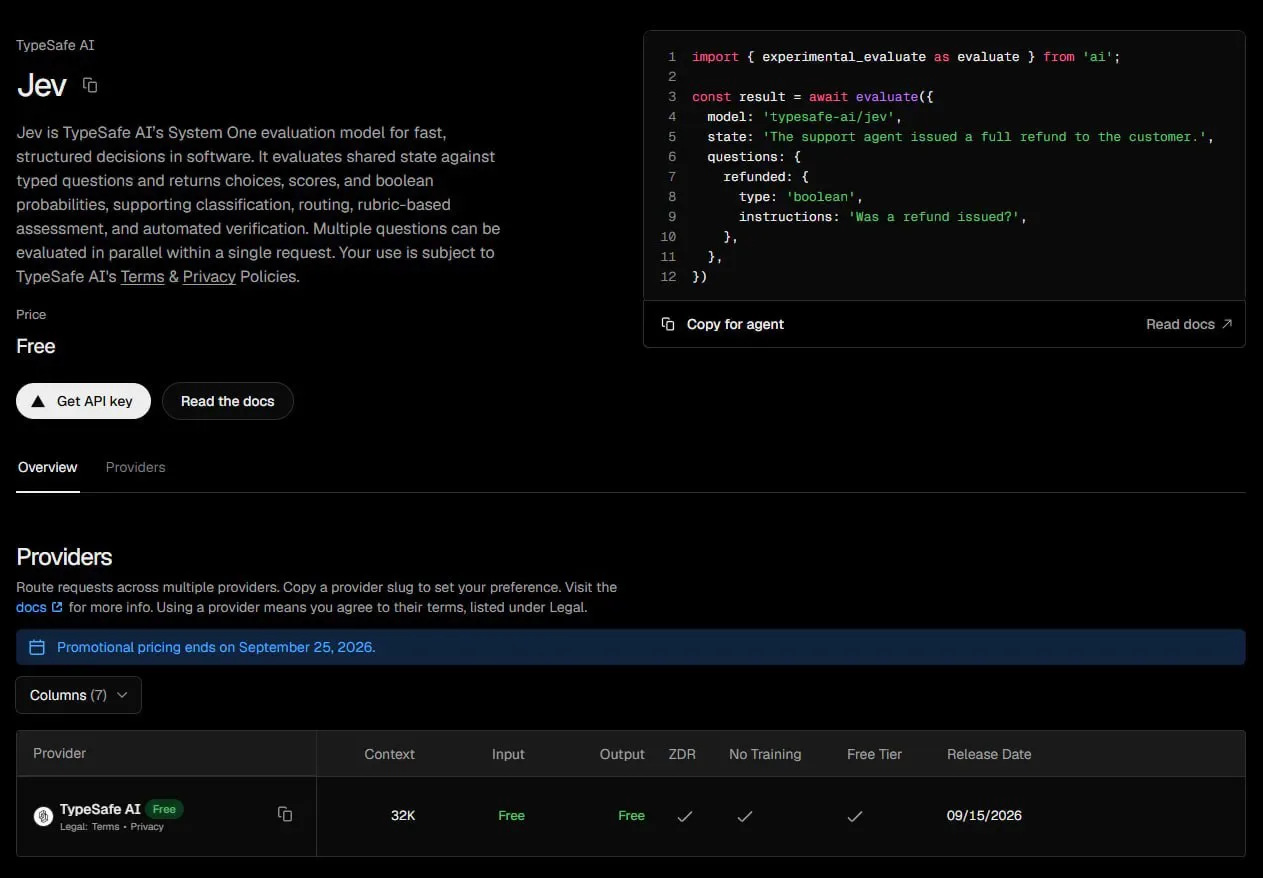
AIAtria Dawn Preview: AI Agents That Learn by Verifying Real WorkAlex Ruiez · 1h · 4 viewsAIHow to Run OpenCreator for Video Translation and DubbingAlex Ruiez · 1h · 3 viewsNewsGoogle's agentic orchestrator doesn't need microservicesAlex Ruiez · 1h · 4 viewsToolsHow to Fix a Hotfix in a Git Worktree Without StashingAlex Ruiez · 1h · 2 viewsNewsMicroservices Usually Mean a Distributed Monolith, Not ScaleAlex Ruiez · 1h · 3 viewsAIHow to Use Jev Free on Vercel AI GatewayAlex Ruiez · 1h · 2 views

Site footer

Revesery

Empowering people to share valuable insights, discover hidden information, and connect with an amazing community of learners and experts.

  • 373Members
  • 507Shares published
  • 0Online now

Explore

  • Explore shares
  • Trending now
  • Top contributors

Company

  • About us
  • Editorial policy
  • Contact
  • Advertise with us
  • System status
© 2026 Revesery
  • Privacy
  • Terms
  • Trust & Safety
  • DMCA
HomeExploreShareToolsProfile
LiveSESecretxxx67joined Revesery· 3 hours ago