How to Find Leaked AWS Keys in Your Own Code
Your site's JavaScript is public, and so is every repo you push. That means a stray AWS access key can sit there for months with nobody noticing.
Two grep one-liners will tell you in seconds whether a key ID is hiding in your own pages or your public repos. Long-term keys and temporary ones show up the exact same way.
What You Need
- A site or repository you own or have permission to scan.
- curl and grep on your machine, plus git for the repo check.
Tutorial
- Scan your live site's JavaScript for key IDs.
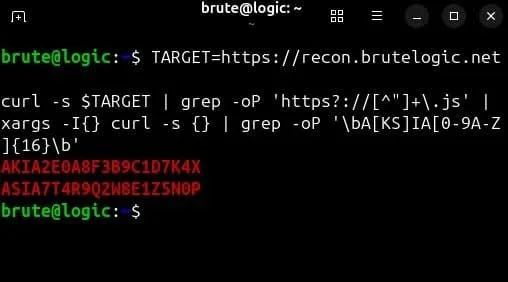
curl -s TARGET | grep -oP 'https?://[^"]+\.js' | xargs -I{} curl -s {} | grep -oP '\bA[KS]IA[0-9A-Z]{16}\b'Swap TARGET for your own URL. The first grep pulls every script address out of the page, then the second checks each one.
- Clone a public repo shallowly and grep it for the same pattern.
git clone --depth=1 TARGET/repo.git /tmp/r && grep -rP '\bA[KS]IA[0-9A-Z]{16}\b' /tmp/rReplace TARGET/repo.git with your repo's address. The --depth=1 flag keeps the download to the latest commit, so it finishes fast.
Wrapping Up
A match means an access key ID is sitting in code anyone can read, and both long-term and temporary keys are easy to leak and easy to abuse. Treat any hit as already compromised and rotate that key rather than just deleting the line. Run the two commands again after a big merge or a deploy and you will catch the next one early.
Does this still work?
Nobody's checked yet
Sign in to tell everyone how it went.
Continue with GoogleBe the first — one tap saves the next person an hour.
It takes 3 reports in 30 days to set the status.
More shares you might like
 AIHow to Claim $100 in Free Entire AI Agent Credits1h6 views
 AIAudio8-TTS-Realistic Tops the Hugging Face TTS Arena1d27 views
 Social MediaHow to Build a Benable List People Actually Save2d28 views
 ToolsHow to Claim 3 Months of Free BotKeep Hosting2d43 views
 Social MediaHow to Grow Pinterest Affiliate Traffic4d36 views
 ToolsHow to Get Free .my.id, .web.id and .biz.id Domains4d36 views

Comments
Join the conversation — sign in to comment.
No comments yet — start the conversation!