
Alex RuiezExpert
ZCode Reportedly Packaged Whole Workspaces, Git History Included
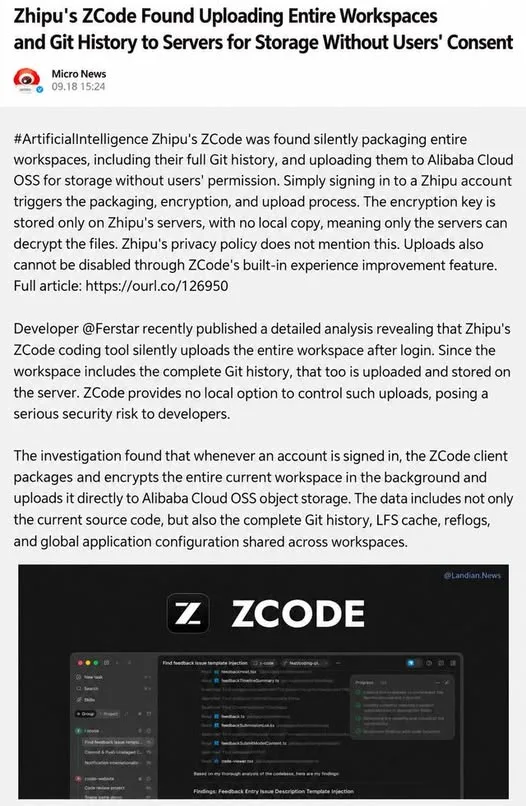
A security disclosure about ZCode says the agent did more than read the files it needed for a task. It reportedly packaged entire workspaces and moved them to the cloud.
If that holds up, the payload was not just your code. It could carry the parts of a project you would never hand to a stranger, including your Git history and whatever secrets sit in your config files.
What Happened
- ZCode is described as an AI coding agent, and the disclosure says the problem was not only that its CLI was sending your code along.
- According to the investigation in the post, ZCode could package the whole workspace: source code,
.git/, Git history, Git LFS objects, reflogs, and even cache and config files. - So the upload was not limited to the files the AI needed for the task. The entire history of the project could end up in the payload.
- The open-source repo for ZCode now shows roughly two commits. There is no clear history showing what existed before, what changed, or what was removed after the security incident.
Why It Matters
- Open source is not automatically safe. You can read the code that is published today, but without the project's Git history, an independent audit of what changed before and after the incident is hard to do.
- The published source code and the binary people actually run are two different things. Reading one does not tell you what the other does.
- AI coding agents have very broad access to your filesystem. Before you give one access to a project, especially one holding
.envfiles, credentials, private repos, or customer data, know what it reads, what it stores, and what it sends to the cloud.
Does this still work?
Nobody's checked yet
Sign in to tell everyone how it went.
Continue with GoogleBe the first — one tap saves the next person an hour.
It takes 3 reports in 30 days to set the status.
More shares you might like
 AIHow to Install hyperresearch for Deep Research in Claude Code1d26 views
 ToolsHow to Set Up Free Temp Email With XTemp Mail1d32 views
 NewsGrabFood Vermuk Bypass: No Working Termux Script Exists2d34 views
 ToolsHow to Self-Host Apps and Databases With Dokploy2d38 views
 News44 AI Agents Ran a Hacking Campaign Against Japan3d48 views
 ToolsHow to Claim Free May.id Domains for a Year4d55 views

Comments
Join the conversation — sign in to comment.
No comments yet — start the conversation!