
Logic Flaws Cause More Damage Than Memory Corruption Bugs
Most of us picture memory corruption when we hear "serious 0-day" — a buffer overflow that lets an attacker run their own code. That is still where the loudest damage lands, and where a lot of hunters spend their hours. But the bugs that give up the most data per find tend to look far duller.
What Happened
Memory corruption bugs like buffer overflows are the ones people call the most impactful 0-days. That is where serious damage happens, and it is where real hunters focus their time.
The claim here is that logic flaws in business workflows ship more damage per bug than the latest memory corruption CVE. The example is one line long: swap a user ID in an API call, and the response comes back with another tenant's records.
Why It Matters
Nothing about that break looks like an attack. There is no crash, no payload, no exploit chain — just a value in a request that was never checked against the person sending it. A memory corruption bug takes skill and patience to turn into something useful. This one takes a wrong number and hands over someone else's data.
So the bug doing the most damage is often the one that looks least like a break-in. If you are hunting, the business workflow may be worth more of your time than the memory bug everyone else is chasing. If you are building, an access check on an object ID is worth the same attention as the memory safety advisory you read last week.
Does this still work?
Nobody's checked yet
Sign in to tell everyone how it went.
Continue with GoogleBe the first — one tap saves the next person an hour.
It takes 3 reports in 30 days to set the status.
More shares you might like
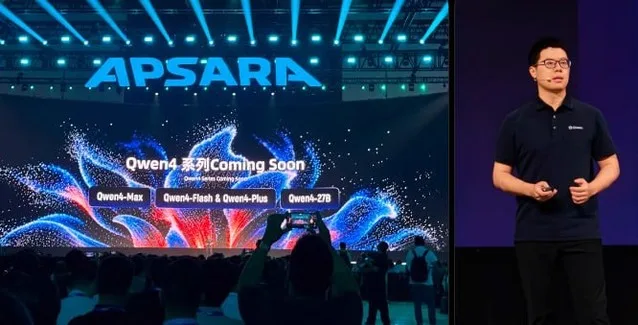 AIAlibaba Reveals Qwen4 Series: Max, Plus, Flash and 27B6h16 views
 AIAnatomy Turns One-Line Machine Prompts Into 3D Wireframes18h17 views
 AIHow to Claim Cursor Pro Credits at MLH Hack Week18h95 views
 Tools226 AI Motion Graphics Examples With Copy-Paste Prompts2d52 views
 ToolsHow to Make Pinterest Pins for Shopee Affiliate With PhotoRoom3d37 views
 MobileHow to Send TikTok Stickers to WhatsApp3d48 views

Comments
Join the conversation — sign in to comment.
No comments yet — start the conversation!