REA: An Open-Source Reverse Engineering Toolkit for AI Agents
Point an AI agent at an app and let it work out how the thing is built. That's the idea behind REA, short for Reverse Engineer Anything — an open-source toolkit that takes an agent from a running app all the way down to native binaries.
It's MIT licensed, it runs on your own machine, and it plugs into Hopper and Ghidra for the deep work.
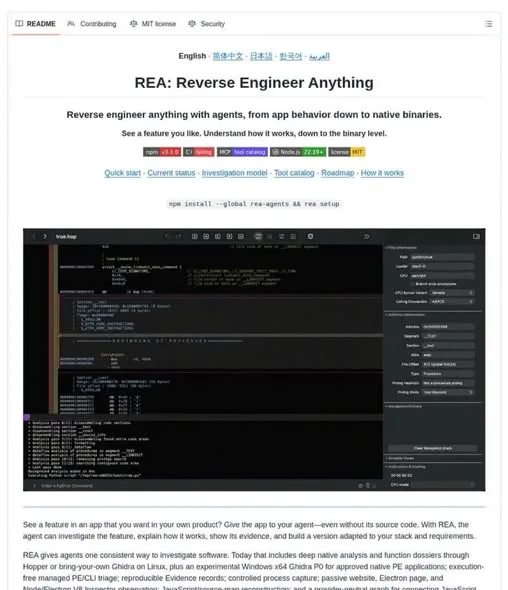
What REA Does
- REA looks at software from two directions: how an app behaves on the surface, and what sits inside the native binary underneath.
- You drive it from a terminal through its CLI, or straight from an AI agent through MCP and a routing skill.
- It decompiles what it finds, then helps recreate the code and structure for your own stack.
- Every run leaves evidence records behind: artifacts, providers, confidence levels, and limitations.
- The analysis happens locally on your machine, not on someone else's server.
- Hopper and Ghidra are both supported on the binary side.
- The whole toolkit is open source under the MIT License.
The loop it's built around runs in one direction: software, then evidence, then understanding, then implementation.
Why It Matters
Instead of an agent only writing new code, it can investigate software that already exists, build an understanding it can back up with evidence, and engineer from that. REA is aimed at developers, AI agent builders, and security researchers who want to dig into how software actually works inside. If you build agents or poke at binaries, this is one to watch.
Wrapping Up
REA gives your agent a way to study existing software and hand you evidence instead of guesses. If that's the kind of work you do, the CLI and the MCP integration are the two doors in. Keep Hopper or Ghidra handy for the binary end.
Does this still work?
Nobody's checked yet
Sign in to tell everyone how it went.
Continue with GoogleBe the first — one tap saves the next person an hour.
It takes 3 reports in 30 days to set the status.
More shares you might like
 ToolsHow to Get a Free .my.id Domain for 1 Year18h21 views
 AISynthetic Heart: Persistent AI Persona Memory Across Chats2d57 views
 ToolsHow to Claim Mobile Legends Diamond Cashback on GoPay2d81 views
 ToolsHow to Redeem McDonald's Coupon Codes in the App3d47 views
 AIHow to Run AI Research Loops With PRAXIST5d97 views
 NewsWebMCP Skill and TypeScript Types for Agent Tooling6d47 views

Comments
Join the conversation — sign in to comment.
No comments yet — start the conversation!